Trade Secret Protection: What “Reasonable Measures” Actually Require
A business does not obtain trade-secret protection by calling information confidential. Under federal law, the owner must take reasonable measures to keep the information secret. Florida law similarly requires efforts that are reasonable under the circumstances. Those standards do not demand a flawless security system, but they do require a protection program that fits the value, sensitivity, and actual use of the information.
That distinction matters because trade-secret disputes often begin with an employee departure, a vendor relationship, a data migration, or a deal that falls apart. By then, the central question is not what the company intended. It is what the company can prove it did before the dispute arose.
Trade-secret status depends on both value and secrecy
The federal Defend Trade Secrets Act defines a trade secret broadly enough to include many forms of financial, business, scientific, technical, economic, and engineering information. But breadth is not automatic protection. Under 18 U.S.C. § 1839(3), the owner must have taken reasonable measures to keep the information secret, and the information must derive actual or potential independent economic value from not being generally known or readily ascertainable through proper means.
The Florida Uniform Trade Secrets Act uses a closely related test: the information must derive independent economic value from not being generally known or readily ascertainable by proper means and must be the subject of efforts that are reasonable under the circumstances to maintain secrecy.
The practical result is a two-part discipline. A company must identify information that has value because others do not know it, and it must behave in a way consistent with that claimed secrecy. Source code, formulas, manufacturing tolerances, nonpublic pricing logic, specialized datasets, product roadmaps, and confidential customer intelligence may qualify. Generic industry knowledge, publicly disclosed features, or information easily reconstructed from public sources may not.
For businesses still deciding whether an innovation should remain confidential or be disclosed in a patent application, Tucker Law’s guide to trade-secret protection versus patent protection explains the strategic tradeoff. The key operational point is that a trade secret can potentially last as long as secrecy does, but the protection can weaken or disappear when the owner’s own practices make the information generally available.
“Reasonable” does not mean identical for every business
The law uses a flexible standard because a small design studio, a medical-device manufacturer, and a software company do not face the same risks or have the same resources. A court may consider the nature of the information, the number and roles of people who need it, how the company shares it, the foreseeable threat, and the cost and practicality of stronger controls.
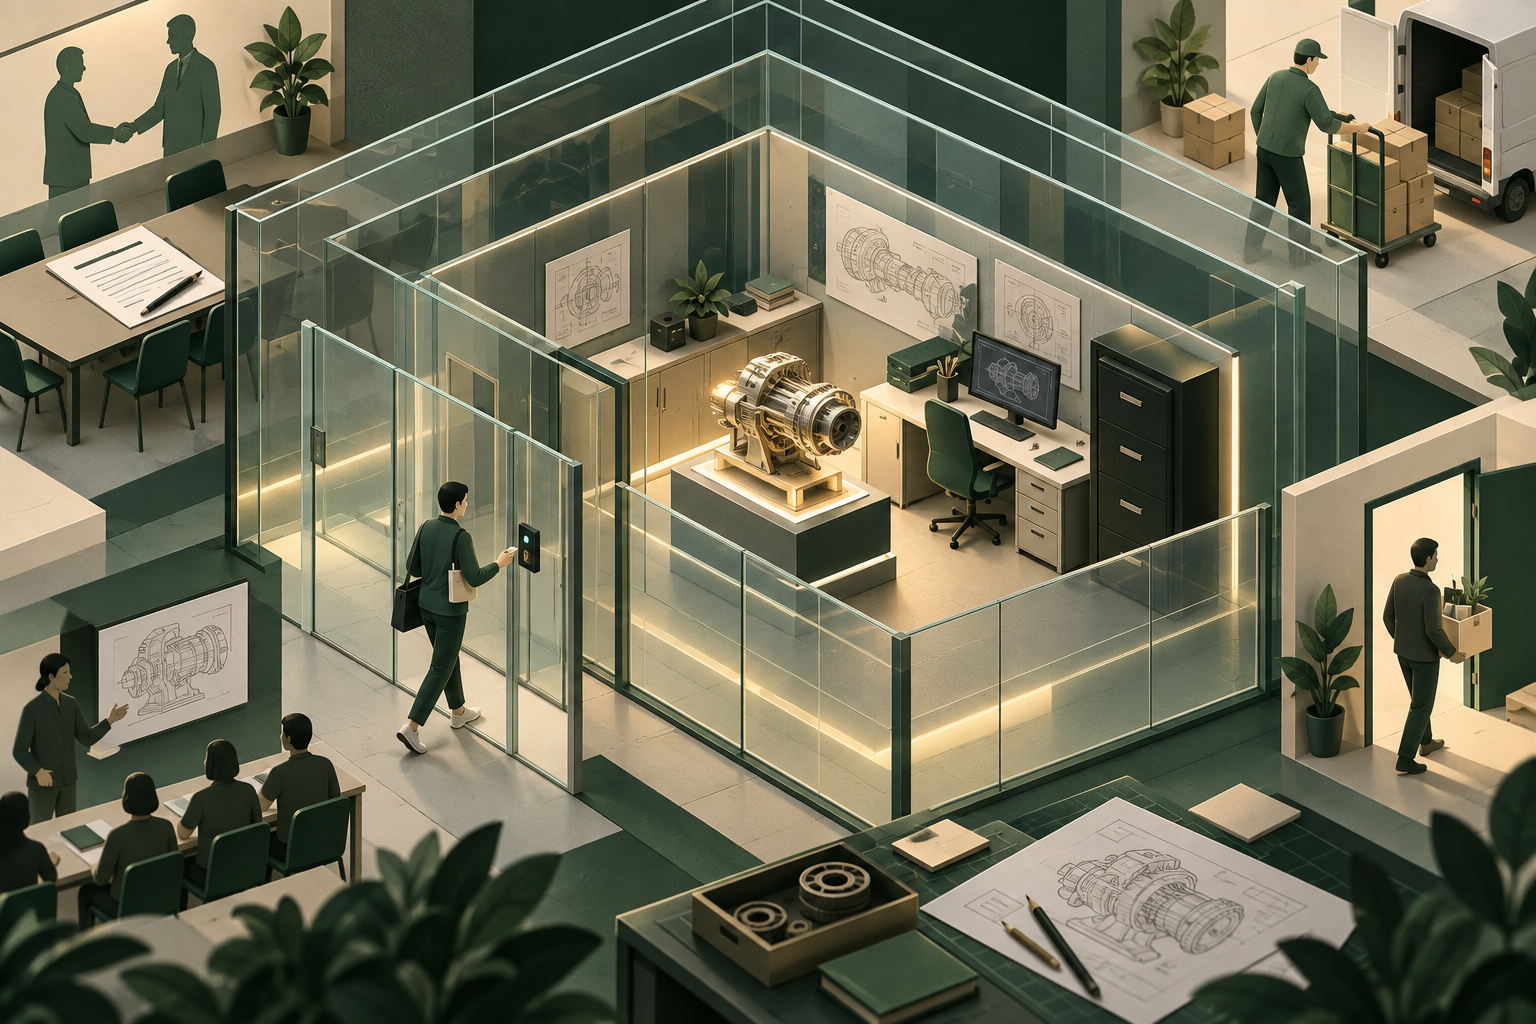
A useful way to think about reasonable measures is as a connected system, not a stack of documents. Contracts communicate duties. Access controls limit exposure. Training helps people recognize the rules. Offboarding closes access when roles end. Logs and records show whether the system actually operated. A weakness in one area can undercut strengths elsewhere.
The Florida lesson from Yellowfin Yachts
The Eleventh Circuit’s published decision in Yellowfin Yachts, Inc. v. Barker Boatworks, LLC offers a concrete warning. Yellowfin limited access to customer information and kept it on a password-protected computer system. The court called those positive steps. Yet it affirmed summary judgment against Yellowfin on its Florida trade-secret claim because other facts undermined those protections.
The company had encouraged the employee to keep the customer information on a personal laptop and phone. He had not signed the proposed employment agreement containing confidentiality provisions. The information was not marked confidential, he was not instructed to secure it on his personal devices, and the company did not ask him to return or delete it after he left. The court concluded that no reasonable jury could find reasonable efforts on those facts.
Yellowfin does not establish a universal checklist. It illustrates something more important: a company’s real workflow can defeat its written or technical safeguards. Restricting a server to a small group may accomplish little if members of that group can freely copy the same files to unmanaged devices. Verbal expectations may be difficult to prove and inadequate when the business tolerates contrary conduct.
Start by defining the information worth protecting
A trade-secret program should begin with an inventory. “Everything confidential” is rarely a useful operating instruction. The business should identify the information that creates a competitive advantage, describe why it is valuable, note where it is stored, and identify who needs access.
This process also helps separate true trade-secret candidates from routine business information. A customer list consisting only of public names and addresses is different from a curated set containing nonpublic buying histories, technical preferences, negotiated pricing, and relationship intelligence. Even then, the compilation’s value and the measures protecting it must be supported with evidence.
Classification should drive treatment. Highly sensitive source code, formulas, or acquisition plans may justify narrowly segmented access and enhanced monitoring. Lower-risk internal material may need ordinary confidentiality controls. Using tiers makes the program more credible and workable than treating every file as equally critical.
Match access to a legitimate business need
Reasonable measures usually include some form of need-to-know access. That does not mean one executive must hold every password. It means employees, contractors, and vendors should receive the access required for their work, and no more.
For digital information, practical controls may include role-based permissions, multifactor authentication, encryption, restrictions on downloads or external sharing, and logs showing who accessed or exported sensitive files. The right mix depends on the system and the risk. A business should also decide whether personal devices are allowed, what security applies to them, and how company information will be removed when access ends.
Physical information still matters. Prototypes, lab notebooks, production instructions, samples, and paper records may need locked storage, visitor controls, sign-out procedures, or restricted work areas. The goal is not theatrical secrecy. It is a consistent boundary between people who are authorized to use the information and those who are not.
Use contracts that fit the relationship
Confidentiality agreements are important, but an NDA alone is not a complete trade-secret program. Agreements should identify protected information with enough clarity to guide conduct, limit use to an authorized purpose, address permitted disclosures, and require appropriate return or destruction when the relationship ends. Employee, contractor, vendor, manufacturing, evaluation, and transaction agreements may require different terms.
When a company is pitching or exploring a deal, staged disclosure can reduce unnecessary exposure. Tucker Law’s guidance on NDAs and pitching an idea and on protecting confidential information in a startup pitch deck addresses that front-end risk.
Federal law adds a commonly overlooked drafting requirement. Under 18 U.S.C. § 1833(b), employers must provide notice of specified whistleblower immunity in agreements governing trade secrets or confidential information with employees. For this provision, “employee” includes contractors and consultants. The notice requirement applies to agreements entered into or updated after May 11, 2016. An employer that fails to provide the required notice may not recover exemplary damages or attorney’s fees under the DTSA in an action against the individual who did not receive notice.
That provision does not authorize ordinary unauthorized access or misuse. It protects certain confidential disclosures to a government official or attorney for reporting or investigating a suspected legal violation, as well as specified sealed court filings. Existing templates should be reviewed for the notice rather than assumed to contain it.
Train people and make the policy real
Employees cannot reliably protect information they do not recognize. Training should explain which information is sensitive, where it may be stored, how it may be shared, what to do with unexpected access requests, and how to report a suspected loss. Short, role-specific training is often more useful than a policy distributed once and forgotten.
Consistency is evidence. If leaders routinely move protected material to personal email, ignore access rules for convenience, or share sensitive presentations without controls, a written policy may have little persuasive force. Periodic access reviews, acknowledgments, and documented remediation show that the company treats the program as an operating requirement.
Build trade-secret protection into the employee lifecycle
Risk changes as people join, change roles, and leave. Onboarding should pair confidentiality obligations with system permissions and training. When responsibilities change, access should change too. Employee-created technology may also raise separate ownership questions, so invention-assignment and confidentiality terms should be coordinated; Tucker Law’s discussion of employee invention rights explains that related issue.
Departures deserve particular attention. A practical offboarding process can include promptly disabling accounts, recovering company devices and records, reviewing recent transfers where justified and lawful, confirming return or deletion obligations, preserving relevant logs, and reminding the departing person of continuing duties. These steps should apply based on risk rather than suspicion alone.
Timing matters. Waiting weeks to revoke credentials or months to request deletion can create both business harm and an evidentiary problem. The company may later need to explain why information now described as critical remained available to someone with no ongoing business need.
Do not overlook vendors, cloud tools, and deal rooms
A business can lose control without an employee doing anything wrong. Vendors, developers, laboratories, manufacturers, consultants, and potential transaction partners may need sensitive information. Before disclosure, the owner should decide what the recipient truly needs, whether subcontractors may receive it, what security measures apply, how incidents must be reported, and when information must be returned or deleted.
Cloud collaboration deserves the same discipline. Public-link settings, inherited folder permissions, dormant accounts, and unrestricted downloads can quietly expand access. Sensitive deal-room or repository permissions should be reviewed during the project and closed when the purpose ends.
Prepare for an incident before one happens
If information is copied or disclosed, a rushed response can make the situation worse. An incident plan should identify who will preserve logs and devices, who can revoke access, who will assess the information involved, and when legal counsel should be contacted. Preservation should come before routine deletion or device reimaging.
The initial investigation should identify the specific information at issue, its location, the people with access, the protection measures in place, and evidence of any acquisition, disclosure, or use. Broad accusations that someone took “all company secrets” can obscure the facts needed for a claim.
Trade-secret law also distinguishes misappropriation from lawful competition. Under the federal definition, improper means include theft, misrepresentation, breach or inducement of a duty to maintain secrecy, and espionage. Reverse engineering, independent derivation, and other lawful means of acquisition are excluded. A protection strategy therefore must account for information that customers or competitors can lawfully learn from a released product.
A defensible program should answer five questions
- What is the trade secret? Identify it specifically enough to distinguish it from public information and general skill or knowledge.
- Why is it valuable? Record how secrecy creates actual or potential economic advantage.
- Who needs access? Limit and periodically review permissions across employees, contractors, vendors, and collaborators.
- What controls apply? Align agreements, technical safeguards, physical controls, training, and device practices.
- What proves the controls worked? Preserve signed agreements, training records, access reviews, logs, exit records, and incident-response documentation.
No single control answers every question, and more security is not always better if it makes normal work impossible. The aim is a proportionate, documented system that the business actually follows.
Trade-secret protection is an operating practice
The most useful time to evaluate reasonable measures is before a key employee leaves, a vendor relationship deteriorates, or confidential files appear elsewhere. A focused audit can uncover unmanaged copies, missing agreements, overbroad permissions, weak offboarding, and gaps between policy and practice while they are still correctable.
Tucker Law advises businesses on intellectual-property strategy, confidentiality arrangements, ownership, licensing, and enforcement. Learn more about the firm’s intellectual property practice, or contact Tucker Law to discuss whether your current safeguards match the information your company depends on.